
EU AI Act · Article 27 · GDPR Article 35
One high-risk AI system can trigger two impact assessments. They are named almost identically, they examine different things, and neither replaces the other.
Companies have known the data protection impact assessment since 2018. It is embedded in processes, templates exist, and the data protection officer knows when one falls due. The fundamental rights impact assessment under Article 27 of the EU AI Act is new — and is regularly mistaken for the same document.
It is not. It addresses a different group, examines a different subject, and carries a different legal consequence. Confusing the two produces one of two errors depending on the direction: believing an obligation is met that was never met, or producing a second document that was not needed.
This article separates the two procedures, shows the overlap the law itself provides for, and places the work in time.
What the data protection impact assessment requires
Article 35 GDPR requires a DPIA where processing is likely to result in a high risk to the rights and freedoms of natural persons. The provision names three categories expressly, and two of them routinely catch AI applications: systematic and extensive evaluation of personal aspects by automated processing on which decisions with legal effects are based, and large-scale processing of special categories of data.
The content is set out in paragraph 7: a systematic description of the processing including its purposes, an assessment of necessity and proportionality, an assessment of the risks to data subjects, and the measures envisaged to address them. The data protection officer is to be involved, the outcome documented, and the assessment updated on material change.
Decisive for the distinction: the DPIA attaches to the processing of personal data. Where an AI system processes none — predictive maintenance on a production line, quality inspection of components, forecasting energy demand — no DPIA obligation arises, even if the system is high-risk under the AI Act.
What the fundamental rights impact assessment requires
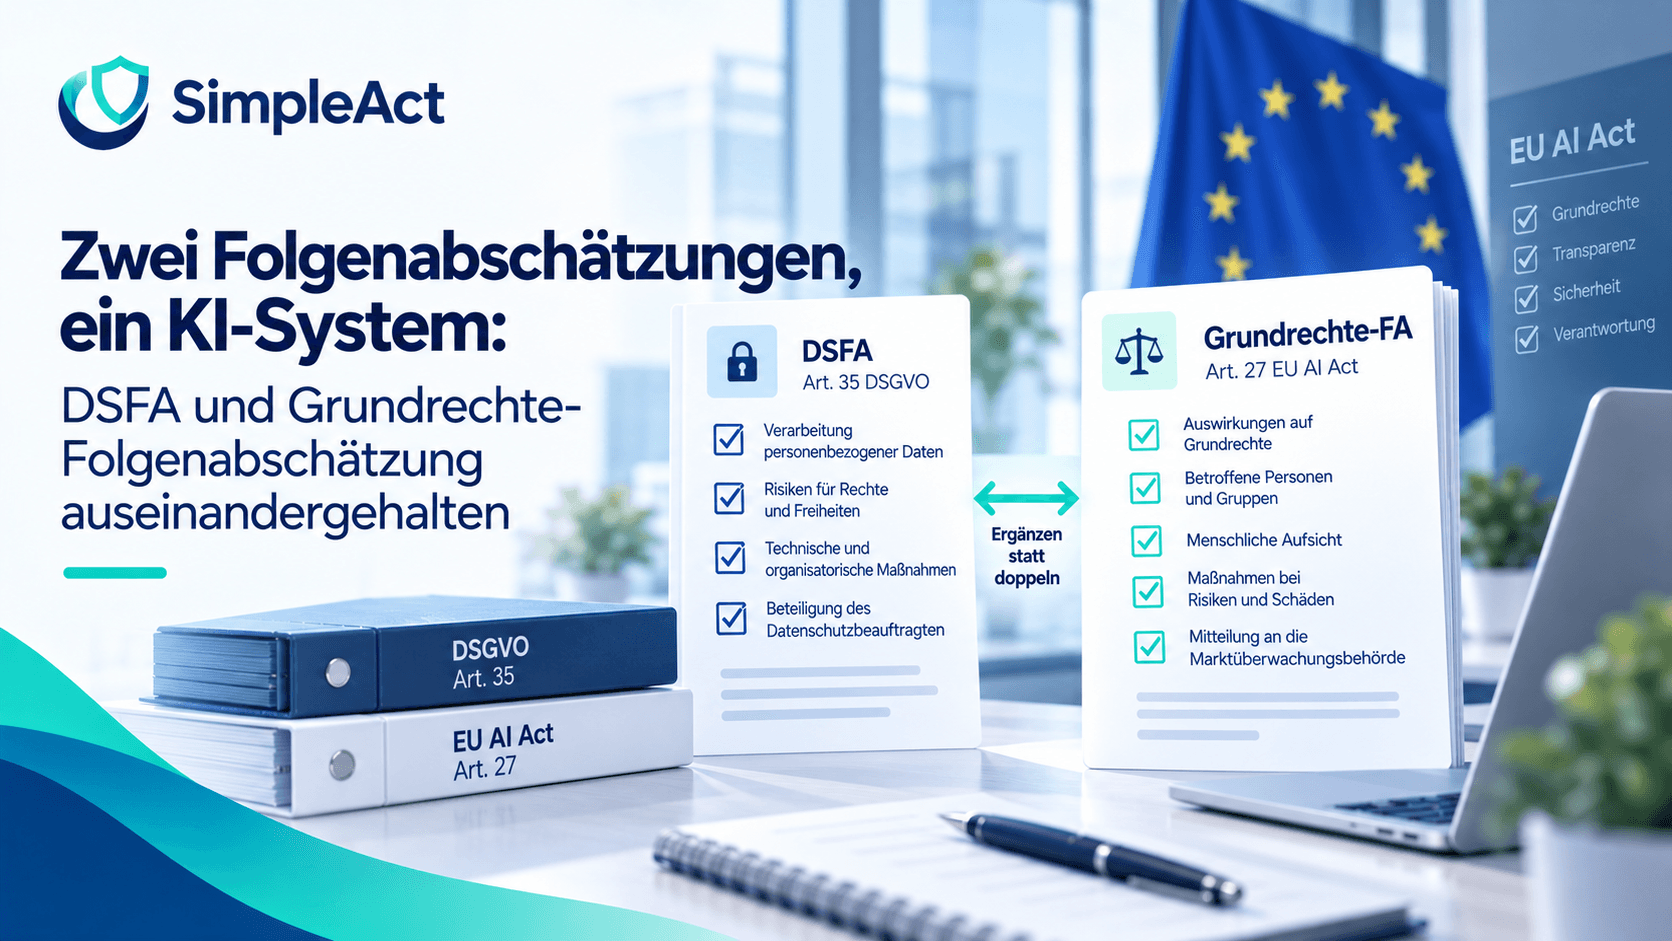
Article 27 AI Act does not oblige every deployer of a high-risk system, but a narrow group: bodies governed by public law, private entities providing public services, and — regardless of legal form — deployers of certain Annex III systems in the financial field, namely evaluating the creditworthiness of natural persons and risk assessment and pricing in life and health insurance.
An industrial company using AI in manufacturing therefore falls outside it. A bank preparing credit decisions with a scoring system does not. That distinction is worth settling before engaging with the content at all.
The content differs markedly from a DPIA. What is required is a description of the processes in which the system will be used, the period and frequency of the intended use, the categories of natural persons and groups affected, the specific risks of harm to those persons, how human oversight will be implemented, and the measures to be taken if those risks actually materialise — including internal complaint channels.
The difference in one sentence: the DPIA asks what happens to a person's data. The fundamental rights assessment asks what happens to the person — including where their data is handled perfectly correctly.
Article 27 has one feature a DPIA does not: the outcome must be notified to the market surveillance authority. The fundamental rights assessment does not stay in the building; it becomes part of a regulatory file. Whoever writes it is writing for a reader outside the company.
Where they overlap, and where they do not
The legislator saw the duplication. Article 27 provides that the fundamental rights assessment complements a data protection impact assessment already carried out, to the extent its obligations are met by it. That is not an exemption but a credit: what has already been examined and documented in substance need not be written twice.
The fourth row is the one that most often raises eyebrows in advisory conversations. A high-risk system with no personal data triggers no DPIA — and, where the deployer belongs to the Article 27 group, a fundamental rights assessment nonetheless. Sorting AI projects through the data protection lens alone misses those cases systematically.
In practice the allocation reduces to three questions, asked in this order. First: for this system, does the company belong to the Article 27 group — a public body, a provider of public services, creditworthiness assessment, or pricing in life and health insurance? Second: is the system high-risk under Annex III or Annex I? Third: does it process personal data, and if so at likely high risk?
Three times yes means both procedures, with the credit applied. Yes to the third question alone means a DPIA only — the most common case in mid-sized companies. Yes to the first two and no to the third means a fundamental rights assessment alone, and that is the constellation most reliably overlooked in practice. Three times no means neither, which leaves the obligations under Articles 26 and 13 untouched.
The timing: December 2027, and the work before it
The Digital Omnibus postponed the obligations for high-risk systems under Annex III by 16 months, to 2 December 2027. For high-risk systems under Annex I — those inside regulated products — 2 August 2028 applies. Article 27 moves with that postponement: where the high-risk obligations bite later, so does the fundamental rights assessment.
The temptation to read that as a pause is understandable and wrong. Three reasons speak against it, and none of them is an appeal to good conduct.
The DPIA was not postponed
Article 35 GDPR has applied since 2018 and applies independently of the AI Act. An AI system processing personal data at high risk today needs a DPIA today — before the processing starts, not on the cut-off date of a different regulation. The postponement touches none of that.
The material comes from the provider
Performance limits, accuracy figures, the oversight measures provided for — the inputs an impact assessment is built from sit in the instructions for use under Article 13. A system procured in 2026 and running in production in 2028 is negotiated in 2026. Fail to demand the documentation at procurement and the assessment later gets written without an evidence base.
Both are due before first use, not on the cut-off date
Both procedures run ahead of deployment. A system going live in December 2027 needs its assessment before that — with all the consultation, alignment and documentation attached. Counting backwards, the start falls considerably earlier than the date suggests.
One source, two documents
Anyone facing both procedures should build them on top of each other rather than side by side. Five components are needed in both documents, and gathering them twice is where the real extra effort sits — not in the writing.
System description and purpose
What the system does, in which process, on what inputs. The DPIA needs it as a description of processing, Article 27 as a description of processes including period and frequency of use. One exercise, two cuts.
The people affected
Who comes into contact with the system, and who is affected by its outputs without operating it? Article 27 expressly asks for groups as well — a perspective missing from many classic DPIA templates.
Human oversight
Named person, means of intervention, state of training. A point of examination in its own right for Article 27, a mitigating measure for the DPIA. The information is identical and should be maintained in one place.
The risks and their sources
Error rates, known biases, the limits of the system. The same facts, two directions of enquiry: risk to the data against risk to the person.
The trigger for an update
Both documents must be refreshed on material change. If both hang off the same events — new purpose, new data source, major provider update — two monitoring duties become one.
What the credit does not cover
Copying an existing DPIA and retitling it "fundamental rights impact assessment" does not satisfy Article 27. What is then regularly missing is precisely the part that goes beyond data protection law: the groups affected, the measures for a risk that has actually materialised, the internal complaint channel — and the notification to the authority. The credit saves gathering effort, not the additional points of examination.
The actual point
The two procedures are not a duplication to be organised away, nor two names for the same thing. They examine the same facts from two directions: one asks about the data, the other about the people.
In practice that means: first establish which of the two applies at all — a two-minute question where the role and classification of a system are documented, and a project where they are not. Then gather the five shared components once and generate both documents from them.
Anyone wanting to know how far off they are needs only a list of their AI systems with role, classification and responsible person. Where that is missing, the impact assessment is not the next topic. The register is.
With SimpleAct
Record once, evidence both.
EU AI Act and GDPR in one platform: register AI systems centrally, classify them rule-based, assign responsibilities and export audit-ready evidence at any time. Made in Germany, hosted in Germany.
Start your AI inventory →This article is for general information only and does not constitute legal advice. Last updated: 4 October 2026.
Tags
Ready to put EU AI Act compliance on autopilot?
SimpleAct helps you inventory AI systems, classify risk, and structure and keep the required documentation up to date.
Kamill Jarzebowski | SimpleAct
Author · SimpleAct Team