
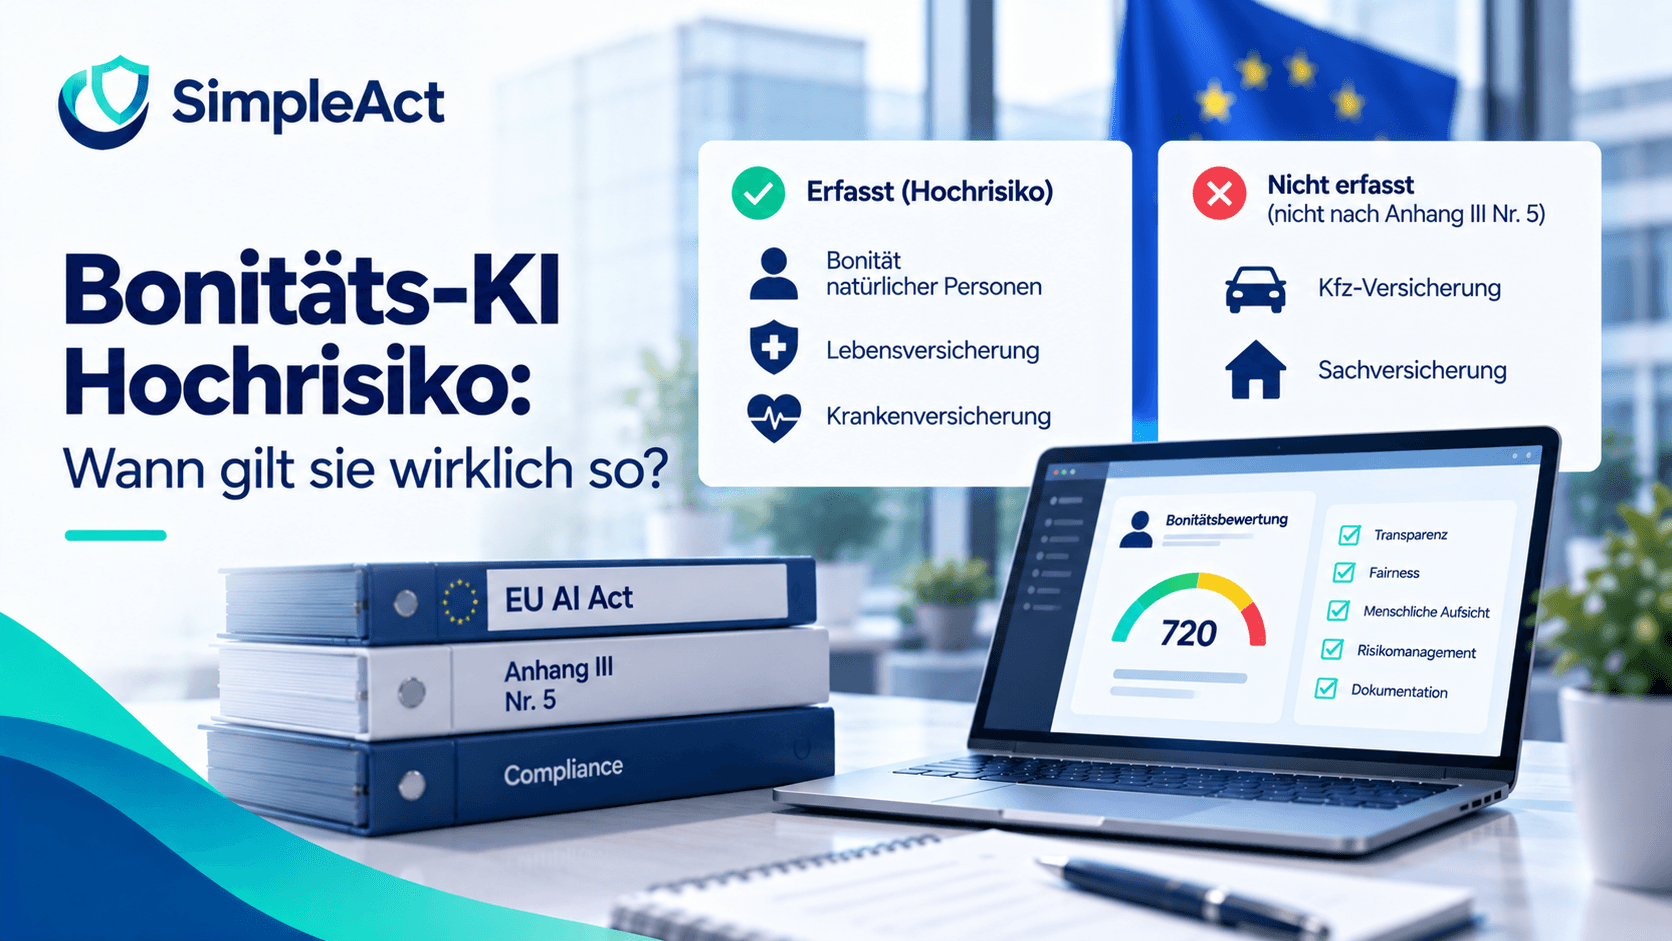
Credit scoring AI high-risk: when does it really apply?
What Annex III point 5 actually covers
EU AI Act · Annex III point 5
Not every AI system at banks and insurers is high-risk. The regulation names two specific cases, and both concern natural persons.
Anyone using a scoring system soon asks whether it counts as high-risk AI. The answer is in Annex III, point 5 of the AI Act, and it is narrower than many assume.
This article shows what points (b) and (c) cover literally, what is expressly excluded and what deployers must observe from 2 December 2027.
Point 5(b): creditworthiness
AI systems for evaluating the creditworthiness or credit score of natural persons. Systems for detecting financial fraud are excluded.
Point 5(c): insurance
AI systems for risk assessment and pricing in relation to natural persons in life and health insurance.
What does Annex III point 5(b) cover for credit scores?
It covers AI systems intended to be used to evaluate the creditworthiness or credit score of natural persons. The word “intended” points to the intended purpose of the system.
Two limits are in the wording itself. Systems for detecting financial fraud are excluded. And credit checks on companies, that is legal persons, are not covered. Sole traders, freelancers and the self-employed, however, are natural persons and therefore covered.
In short: What matters is who is being assessed. Private individuals and sole traders: point (b). Legal persons such as a limited company: not covered by point (b).
An example from the mid-market: an online retailer has the creditworthiness of private customers assessed automatically before a purchase on invoice. The high-risk item here is the scoring system. The retailer is a deployer only if it uses the system itself. If an invoice-payment service takes on the default risk and decides itself, the service is the deployer. A pure fraud check, for example of identity or delivery address, is excluded. This is an interpretation of the wording, not an authority’s ruling. Check the intended purpose in the provider’s documentation.
If admission to purchase on invoice depends decisively on the score, Art. 22 GDPR may also apply (CJEU C-634/21, SCHUFA).
What applies to insurance under point (c)?
Point (c) names risk assessment and pricing in life and health insurance, each in relation to natural persons. Other types of insurance are not listed there.
Named in point (c)
Life and health insurance: AI for risk assessment and pricing in relation to natural persons.
Not named in point (c)
Motor, property, liability and household insurance, and policyholders who are not natural persons. Point (c) does not name them.
That does not mean such systems are legally irrelevant. Data protection law and other rules apply regardless. High-risk status can also arise from another point of Annex III, for example if an authority uses it to decide on public benefits (point 5(a)). The profiling rule in Art. 6(3) does not change that: it applies only to systems already listed in Annex III and does not make a motor pricing model high-risk.
Which systems are high-risk and which are not?
The table classifies typical systems by the wording of Annex III point 5. It does not replace an assessment of the specific system.
Is every kind of scoring high-risk?
Common misconception
“Any AI in finance and insurance is high-risk.” The correct position: Annex III point 5 covers only creditworthiness assessment of natural persons (point (b), excluding fraud detection) and risk assessment and pricing in life and health insurance (point (c)).
Where a system falls under Annex III, there is an exemption under Art. 6(3). It applies only if there is no significant risk to health, safety or fundamental rights and one of the four listed conditions is met. Systems that profile natural persons, however, are always considered high-risk.
Profiling is any automated processing of personal data to evaluate personal aspects, including economic situation or reliability. According to the CJEU, credit scoring of natural persons is profiling (C-634/21, para. 47). On that reading, the exemption under Art. 6(3) is therefore practically ruled out for systems under point (b).
What deployers must observe from 2 December 2027
The high-risk obligations for systems under Annex III apply from 2 December 2027 (Art. 113(3)(c) as amended by the Omnibus). Before that the date was 2 August 2026.
Deployer obligations under Art. 26
Use in line with the instructions, human oversight by competent persons, monitoring of operation and keeping logs for at least six months.
Fundamental rights impact assessment under Art. 27
Always required for deployers of systems under point 5(b) and (c): before first use, covering purpose, affected persons, risks, oversight and complaint channels. Parts of a data protection impact assessment may be reused by reference.
An overview of deployer duties is on our page about deployer obligations under the AI Act. On the question of provider versus deployer, read EU AI Act technical documentation: Who must prepare it?.
Four steps to classify your scoring system
The steps are a recommendation. The regulation does not prescribe a sequence.
Record systems with an assessment function
Where does software assess creditworthiness, default risk or insurance risk, including as a building block of a purchased tool?
Clarify who is assessed
Natural persons or companies? Sole traders count as natural persons. Classification under point (b) depends on it.
Check the intended purpose with the provider
What is the system intended for according to the provider? Ask for it in writing.
Record the result and reasoning
If high-risk: plan deployer duties and the fundamental rights impact assessment. If not high-risk: document the reasoning.
The point that matters
High-risk is not a blanket verdict for creditworthiness and insurance. What counts is who is assessed and the type of insurance.
The classification can only be evidenced if you have recorded for each system who it assesses and what it is intended for. That is also the basis for every later obligation.
With SimpleAct
Record who an AI system assesses and what it is intended for in one place.
EU AI Act and GDPR in one platform: record AI systems centrally, classify them by rules, assign responsibilities and export audit-ready evidence at any time. Made in Germany. [Hosting-Satz nach K6]
Record your AI systems now →Sources
Regulation (EU) 2024/1689 (AI Act), Art. 6, 26, 27, Annex III point 5 · Regulation (EU) 2026/1744 (Digital Omnibus on AI), Art. 1 point 40
This article is for general information only and does not constitute legal advice. Last updated: 19 October 2026.
Tags
Ready to put EU AI Act compliance on autopilot?
SimpleAct helps you inventory AI systems, classify risk, and structure and keep the required documentation up to date.
Yannick | SimpleAct Team
Author · SimpleAct Team